Expense tracking without SMS permission
You can track your spending without giving any app access to your text messages. SMS is just one source of transaction data — your bank emails you the same alerts, an Account Aggregator connection can fetch them with your consent, and you can tell an app yourself in a sentence. That matters because SMS permission on Android is not scoped to your bank: it grants the whole inbox, one-time passwords included. Google itself treats it as highly sensitive and allows it only for a short list of uses.
Last updated
What you are actually agreeing to
When a budgeting app asks for SMS access, the request in your head is “read my bank alerts.” The request the operating system grants is “read my messages.” There is no middle setting. Android does not let you approve access to texts from HDFC and withhold access to everything else, because permissions are granted per-category, not per-sender.
So the actual scope includes:
- Your one-time passwords. Every OTP for every bank, exchange, wallet and login you use arrives as a text.
- Messages from people. Family, your doctor’s clinic, a lawyer, a landlord.
- Everything else. Delivery codes, appointment reminders, ticket confirmations, and whatever else you have ever received.
None of that is an accusation against any particular app. Most apps asking for it are doing exactly what they say. But you are trusting a promise you have no way to verify, and the thing you are staking on it includes the codes that protect your bank accounts.
The safest permission is the one an app never needs. If a product can deliver the same automation without touching your inbox, that isn’t a marketing difference — it removes the question entirely.
Google agrees it’s sensitive
Google restructured Play policy around it. Under the current rules, SMS and Call Log permissions sit in a restricted category: an app generally must be the device’s default SMS, Phone or Assistant handler to request them, use must be limited to documented core functionality essential to the app’s primary purpose, and anything outside the pre-approved list requires a declaration reviewed by Google. Apps that don’t meet the policy, or that skip the declaration, can be removed from the Play Store.
A finance tracker is not your default messaging app, so it needs an exception. Google’s list of exceptions does include “SMS-based money management” — apps that track and manage a budget — so a budget app can apply, and some are approved after a case-by-case review. The same policy says budgeting apps may not share non-financial or personal SMS history. But an approved exception doesn’t shrink what the permission grants once you tap accept: the app can still read the whole inbox, and you are trusting it to look only at the bank alerts.
If you are weighing up an app that asks for it, there is a five-step way to judge whether granting it is safe rather than guessing.
An Indian expense tracker whose automation is SMS-based also has a permanent platform problem on iPhone, where the API does not exist in any form. That’s a separate argument, covered on expense trackers for iPhone in India.
The alternatives, compared honestly
These are the realistic ways an app can learn that you spent money, and what each one costs you in access.
| Method | Automatic | What you hand over | Sees your OTPs |
|---|---|---|---|
| SMS parsing | Yes | Your entire message inbox | Yes |
| Notification reading | Yes | Every notification from every app | Often |
| Net-banking login | Yes | Bank credentials | Effectively yes |
| Account Aggregator | Yes | Regulated, revocable consent to account data | No |
| Email alerts (read-only) | Yes | Read-only access to your mail | No |
| Statement import | No | Nothing ongoing | No |
| A sentence, typed or said | No | Nothing (the microphone, if you speak it) | No |
| Manual entry, field by field | No | Nothing | No |
The Account Aggregator framework is different: it is regulated, consent-based, revocable, and genuinely better designed than screen-scraping a login. Its trade-offs are coverage and breadth — not every institution is live on it, and the consent covers account data rather than a single alert.
Email parsing sits in a useful spot on that table. It is fully automatic, it never sees a one-time password, and it needs no credentials. What it gives up is completeness: it can only see accounts that actually email you.
Telling the app yourself sits at the other end. It needs no access at all and it is the only method that catches cash, splits and transfers correctly; the cost is that you have to do it. Whether that cost is a form per purchase or a five-second sentence depends entirely on how the app is built — what an automatic feed misses goes through it.
How TLDR Classic works without it
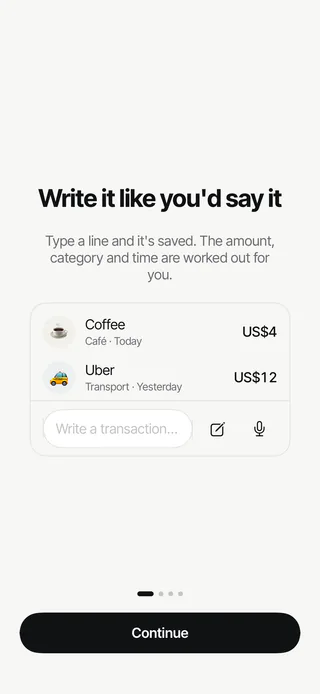
TLDR Classic does not ask for SMS permission, because nothing in it reads your messages. You type what you spent the way you’d say it (“₹250 auto and ₹180 chai” becomes two entries) and it’s saved, or you tap the microphone, say it, and check the confirm card. On Android the microphone is the only permission voice entry asks for (an iPhone also asks for speech recognition, which runs on the phone), and you can switch it off in your phone’s settings and keep typing.
It does not ask for your net-banking credentials, does not see your OTPs, and has no connection to your accounts, so there is nothing to revoke and no route through which money could move. Speech is turned into text on your phone, and the audio is never recorded or sent. What leaves your phone for each feature is set out on the security page; your rights over the data, and how to exercise them, are in the TLDR Classic privacy policy.
For UPI payments there is a quicker way in on Pro: share the payment screenshot to TLDR Classic and it is read on your phone for you to confirm. The screenshot is never uploaded.
The honest limitations of telling it yourself
- You still have to log it. A sentence takes seconds, but a day you forget is a gap until you catch up from your UPI history.
- It won’t find a subscription you forgot about. Check your UPI AutoPay mandates and card statement for those; that is the one job a feed does better.
- It won’t reconcile to the rupee. You will round, and you will miss the odd chai. For budgeting, that is close enough.
What to check before you grant anything
- Read the permission list before installing, not after. On Android, the Play listing’s data-safety section and the permission prompts tell you more than the marketing page does.
- Ask whether the permission is needed for the feature you want. If tracking works without it, granting it buys you nothing.
- Check whether access is read-only, and whether you can revoke it independently. A connection you can cut from Google’s side, not just from inside the app, is a meaningfully stronger position.
- Find out how the app earns. A free tracker is monetising something. Knowing what tells you how your data is likely to be used.
- Never share an OTP, PIN or password with anyone. No legitimate finance company will ask you for one — TLDR Money never will.
Keep reading
Questions worth asking
Can I track expenses automatically without giving SMS permission?
Yes. SMS is one source of transaction data, not the only one. Your bank and card issuer also email transaction alerts, and an app can read those instead — which gives you automatic categorisation without any access to your text messages. Other routes exist too: an Account Aggregator or bank connection, or importing statements. Telling the app yourself — typing a sentence or saying it — needs no data access at all, and is quick enough to keep up if the app is built for it.
What does SMS permission actually give an app access to?
Your entire message inbox, not just the bank alerts. That includes one-time passwords, messages from your doctor or lawyer, delivery codes, personal conversations, and anything else that arrives by text. Android has no way to grant access to only the messages from your bank. The permission is all-or-nothing, which is why the scope is so much wider than the stated purpose.
Is it safe to give an expense app SMS access?
It depends entirely on the company, and you cannot verify it from the outside. Google treats SMS as highly sensitive: under Play policy an app generally must be the device’s default SMS handler, or hold an approved declared exception, to request the permission at all, and non-compliant apps can be removed from the Play Store. The permission also exposes your one-time passwords, which is the specific reason security guidance tells people to be careful with it. If an app can do its job without the permission, that is strictly safer than trusting that it will behave.
Why do so many Indian expense apps ask for SMS permission?
Because in India nearly every UPI debit, card spend and salary credit generates a text message, in a predictable format, from a small set of senders. That made the SMS inbox the cheapest reliable transaction feed in the country — no bank partnership, no integration, no approval needed. It is a sensible engineering choice from the app’s side. It just means the user carries the privacy cost of the shortcut.
Does TLDR Classic ask for SMS permission?
No. In TLDR Classic you type what you spent the way you’d say it, or say it, so the app has no need to read your messages. It does not ask for SMS permission or your net-banking credentials and does not see your one-time passwords, and with no connection to your accounts it cannot move money, place a trade or open an account.
Track it in a sentence. No SMS permission.
Type it or say it, and it’s saved. No access to your texts, your OTPs or your bank login. Every new account starts with 30 days of Pro, no card needed.
Sources
- Google Play Console Help, “Use of SMS or Call Log permission groups” — support.google.com
- Google Play Console Help, “Permissions and APIs that Access Sensitive Information” — support.google.com
- Android Developers, “Permissions used only in default handlers” — developer.android.com
- Android Developers Blog, “Reminder: SMS/Call Log Policy Changes” — android-developers.googleblog.com
Platform and store-policy behaviour described here reflects Android and Google Play as of October 2026 and can change. This is an explanation of how permissions and transaction capture work, not advice about your own money.